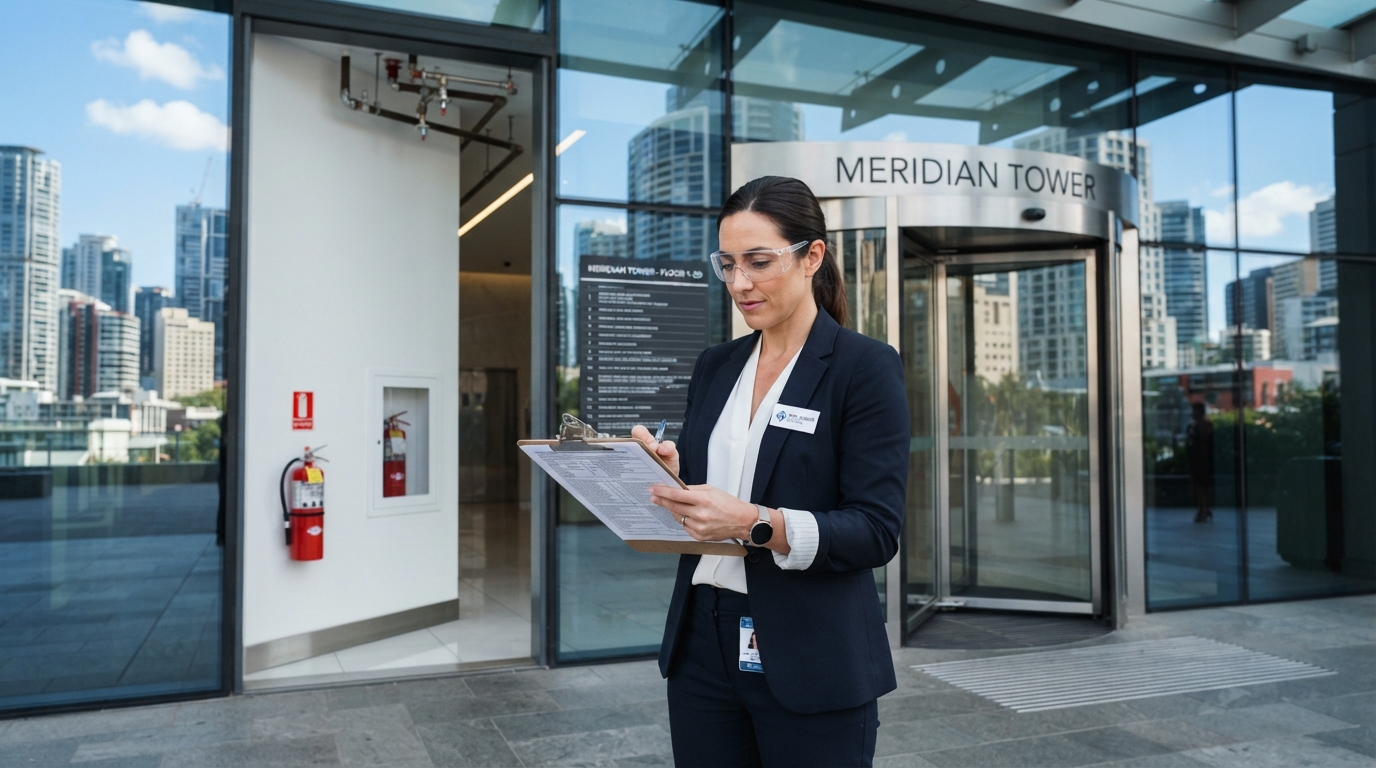
A property owner’s fire-protection measures and location can change the way an insurer views the same building. Risk assessment helps us understand why.
Across the U.S. property and casualty insurance market, assessments support decisions for policyholders and insurers. They help insurers judge exposures before setting coverage and prices. They also help businesses plan for business continuity and reduce losses from natural disasters.
Changing catastrophe, technology, and data risks call for structured analysis and informed judgment. A consistent approach helps teams compare similar exposures, explain their decisions, and spot gaps in risk management. It also gives policyholders a clearer view of the controls that may affect their coverage decisions.
A useful assessment turns those details into decisions about coverage, price, and managing the insurer’s own exposure.
Key Takeaways
- Assessments help insurers and policyholders understand exposures.
- Risk evaluation compares likelihood and impact with set criteria.
- Property details and safeguards can shape coverage and price.
- Methods should fit the decision and the quality of evidence.
- Regular reviews keep assessments useful as conditions change.
What Does Risk Assessment Mean in Insurance?
In insurance, risk assessment helps us judge what could cause a claim, how likely it is, and how costly it could be. It supports risk management, the wider work of understanding and responding to uncertainty.
In P&C insurance, that work commonly moves through three stages: risk identification, risk evaluation, and risk mitigation. Assessment supports underwriting decisions, but it does not make the final decision by itself. An underwriter also considers policy terms, business goals, and the insurer’s ability to take on the exposure.
Assessment supports underwriting decisions, but it does not make the final decision by itself.
Risk identification means finding events or conditions that could lead to a loss. Analysis then estimates their likelihood and impact, using evidence such as records, inspections, or expert judgment.
Risk evaluation = comparing an identified risk’s likelihood and impact with defined criteria to decide whether it needs action. The criteria may reflect limits, business priorities, or the insurer’s tolerance for loss.
Risk mitigation means taking steps to avoid, reduce, share, or prepare for a risk. Together, these stages inform whether to insure an exposure, which coverage and terms to offer, and how much to charge.
Risk evaluation is the comparison of likelihood and impact against decision criteria, not simply a rating of “high” or “low.” A business may use that comparison to choose controls, while an insurer uses it to support its coverage and pricing decisions.
For example, a business may have a water-loss exposure that deserves a new leak alarm. An insurer may weigh the same exposure alongside other evidence before deciding whether to offer coverage.
Those decisions can differ because policyholders and insurers have different roles, resources, and levels of risk tolerance. Treat the result as decision support, not as a substitute for underwriting judgment.
How Does an Insurer Evaluate a Property Risk?
A property’s construction, location, claims record, and safety systems together shape its insurance profile. Underwriters use them to estimate the probability and potential severity of a loss.
They review construction type, building age and condition, intended use, replacement value, and claims history. A mismatch between the declared use and actual operations can change the risk assessment. A warehouse that stores flammable goods presents different concerns than one holding furniture.
Location analysis considers natural hazards, local infrastructure, access to fire and rescue services, and risks from nearby properties. Exposures can include fire, water damage, storms, hail, electrical faults, machinery breakdown, and explosions.
Inspectors also review alarms, sprinklers, fire compartments, maintenance, emergency plans, and staff training. These safeguards can reduce the chance of a claim or limit its severity, but only when they work and match the way the property operates.
Use this practical inspection checklist before an application or renewal:
- Confirm the building’s use and replacement value.
- Verify its construction type and current condition.
- Map local hazards and neighboring exposures.
- Inspect fire, security, and prevention controls.
- Reconcile claims history and requested deductibles.
Underwriting can accept a risk, accept it with modified terms, or reject it. Terms may change through limits, exclusions, deductibles, or a request for stronger safeguards.
Pricing estimates claim frequency and severity using construction, location, use, insured value, deductibles, claims history, and security measures. A gross premium can include expected losses, administrative and acquisition costs, reinsurance costs, risk premiums for volatility or catastrophe losses, and profit margin.
For personal auto coverage, location, driving history, vehicle, limits, and deductibles also affect prices. Drivers can compare online car insurance quotes using the same coverage choices.
Before submitting an application, check that the declared use, replacement value, and protection systems match the property as it is actually operated.
How Do Insurance Risk Assessment Methodologies Differ?
The best starting point is the kind of answer the insurer needs: a ranked concern, a comparable score, or an estimate of financial loss. Evidence quality helps determine which method can support that answer.
Examples of insurance risk assessment methodologies include qualitative, quantitative, and semi-quantitative approaches. Specialized methods work best when they address a defined exposure. A score does not become a loss estimate just because it uses numbers.
Qualitative assessment for limited data
Qualitative assessment uses descriptions such as high, medium, and low. An expert may judge a threat severe but unlikely when evidence is sparse or difficult to price.
This approach is useful for early review and hard-to-measure exposures. Its weakness is that different reviewers may assign different ratings unless they use shared criteria and clear examples.
Quantitative assessment for measurable losses
Quantitative analysis uses numerical data and models to estimate probability distributions or expected loss. It can help compare financial outcomes when past loss records and model inputs are reliable.
Specialized approaches include FAIR, which estimates information risk using threat frequency, vulnerability, and loss data. Monte Carlo simulation runs many possible combinations of uncertain variables to show outcome ranges and their associated probabilities.
Semi-quantitative scoring and specialized assessment
Semi-quantitative methods apply numeric scales to expert judgments. They can create comparative priority scores, but those scores are not true monetary values.
Other method families include asset-based, vulnerability-based, and threat-based assessment. The table shows common uses and the limits of each approach.
| Method | Typical inputs | Output | Best fit |
|---|---|---|---|
| Qualitative | Expert judgment and descriptive ratings | High, medium, or low | Sparse or hard-to-price evidence |
| Quantitative | Historical loss data and statistical models | Probability distributions or expected loss | Measurable financial losses |
| Semi-quantitative | Expert judgment and numeric scales | Comparative priority scores | Ranking risks across a portfolio |
| FAIR | Threat frequency, vulnerability, and loss data | Annualized loss range | Financial view of information risk |
| Monte Carlo simulation | Probability distributions across variables | Outcome ranges and associated probabilities | Uncertainty across linked variables |
Examples of insurance risk assessment methodologies range from broad ratings to financial models. Match the method to the evidence, and use a qualitative rating when evidence is thin. Reserve monetary precision for cases with data that can support it.
When Should Insurers Use Specialized Analysis Techniques?
A machinery failure that interrupts production calls for a more focused analysis than a broad high-medium-low rating. A specialized method can trace how the failure starts and what follows.
These techniques help teams examine connected causes, effects, and controls. Use them when a specific process, machine, or event needs more detail than a broad risk rating can provide.
Failure analysis for process and equipment breakdowns
Failure Mode and Effects Analysis (FMEA) lists ways a process or piece of equipment could fail, then considers the effects of each failure. Failure Mode, Effects, and Criticality Analysis (FMECA) adds a focus on how critical each failure may be.
Both methods help teams rank failure modes for risk mitigation. ISO/IEC 31010’s risk assessment techniques support choices that fit an organization’s needs and context. Its implementation guide covers planning, information management, techniques, review, and use of results.
A team might find that one pump failure could stop production, while another creates only a short delay. The first may need a backup or faster repair plan.
Cause-and-consequence analysis for complex scenarios
Fault tree analysis works backward from an unwanted event, such as a plant fire, to identify combinations of causes. Bowtie analysis maps causes, a central event, consequences, and controls on either side.
These methods can reveal where several threats rely on the same weak control. FAIR can help estimate financial loss for defined information risks, while Monte Carlo simulation can explore uncertainty across many linked variables.
Structured techniques for expert and stakeholder input
Structured input can make risk identification more consistent across teams. Common techniques include:
- Brainstorming
- Delphi technique
- Nominal group technique
- Structured or semi-structured interviews
- Surveys
Checklists, classifications, and taxonomies also help teams spot known threats. A checklist is not a complete analysis when an exposure is new or interconnected. It may miss links that no existing item describes.
For expert input, teams should record disagreements and the evidence behind their choices. A shared rating can hide important differences if reviewers do not discuss why they reached it.
Prioritize the failure modes that combine serious consequences with credible likelihood and weak controls.
How Should We Choose a Risk Assessment Methodology?
Choose the method backward from the decision the assessment must support. Start with the decision, then consider the evidence, people, and time available.
Business objectives and scope set the boundaries. A review meant to support a coverage change may need different detail than one meant to compare risks across an enterprise.
Data quality matters because weak or incomplete records can make a detailed model misleading. Staff expertise also affects whether a team can use the method and explain its results.
Time, resources, and regulatory requirements can narrow the options. A critical risk assessment should rank exposures by potential impact and likelihood, while considering tolerance and the organization’s ability to act.
Use the simplest approach that can produce a useful, defensible decision. The table links common needs to suitable approaches and cautions.
| Assessment need | Suitable approach | Useful output | Limitation to watch |
|---|---|---|---|
| Sparse data and expert judgment | Qualitative assessment | Descriptive ranking | Subjectivity |
| Financial loss comparison | Quantitative analysis | Probability or expected-loss estimates | Needs reliable data |
| Cross-risk prioritization | Semi-quantitative scoring | Comparable scores | Risk of false precision |
| Process or equipment failure | FMEA or FMECA | Ranked failure modes | Needs complete failure analysis |
Scalability matters when an assessment will be repeated across many sites or business units. A method that works for one team may be too costly or slow across a whole portfolio.
Compliance needs can also shape the record, review, and approval process. Teams should confirm that the method supports required decisions without claiming more certainty than the evidence allows.
If a score cannot change a coverage, control, or capital decision, simplify the assessment rather than adding complexity.
What Are the Main Steps in a Risk Assessment?
A repeatable assessment starts by fixing the decision, scope, and criteria before collecting evidence. Clear boundaries help teams avoid gathering details that cannot affect the result.
A practical four-step sequence is prepare, conduct, communicate, and maintain. Risk identification, analysis, evaluation, and treatment fit within the wider risk management cycle.
NIST SP 800-30 Rev. 1 guides risk assessments for federal information systems and organizations. It connects assessment at organizational, business-process, and system levels with the wider risk management hierarchy.
- Prepare by setting scope, criteria, roles, and available information.
- Conduct by identifying exposures, estimating likelihood and impact, and evaluating priorities.
- Communicate by recording conclusions, assumptions, and actions for decision-makers.
- Maintain by updating the assessment when operations, evidence, or conditions change.
Preparation should name the decision owner and the people who will review evidence. It should also set criteria before the team sees results, which helps limit bias.
During the assessment, teams identify what could cause loss, analyze possible outcomes, and compare findings with criteria. Treatment then sets a response, such as reducing an exposure or accepting it within limits.
Communication makes the result usable. A concise record can show the exposure, rating, evidence, assumptions, action, owner, and review date.
For example, a business can document a water-loss exposure in its risk register. The team can rate likelihood and impact, assign a leak-control action, name an owner, and set a review trigger.
Maintenance matters when a new claim, building change, or control failure alters the evidence. An assessment can also link risks across company, process, and system levels.
Record assumptions and review triggers with each finding so another decision-maker can understand why the rating may change.
What Data and Tools Make Assessments More Useful?
A hazard map can locate a property in an exposed area, but it cannot confirm whether its sprinkler system works. Tools add context, not proof of site conditions.
Geographic information systems (GIS) combine location data with hazard layers. Catastrophe models use hazard, building, and policy information to estimate potential losses.
Reliable, current, consistent records matter more than large volumes of disconnected data. Predictive analytics can examine claims and operational data for patterns, while sensors can flag changing conditions.
| Tool family | Principal inputs | Assessment output | Decision supported |
|---|---|---|---|
| GIS | Location and hazard layers | Mapped location exposure | Property accumulation and site review |
| Catastrophe models | Hazard, building, and policy information | Modeled loss estimates | Catastrophe planning |
| Predictive analytics | Historical claims and operational data | Emerging patterns | Portfolio review |
| IoT monitoring | Sensor readings for leaks, fire, or security | Alerts about changing conditions | Prevention and reassessment |
Internet of Things (IoT) sensors can monitor water leaks, fire conditions, and security. An alert may prompt a site visit or a new assessment, but it does not explain every cause.
Predictive models can help teams spot patterns across claims that are hard to see one file at a time. Their results still depend on how well the input data reflects current operations and risks.
A common mistake is treating a model output as a verified site inspection or a guaranteed loss forecast. Model results are estimates that depend on assumptions and input quality.
Validate important model inputs against current property and policy records before relying on the output.
How Do Catastrophe and Climate Risks Change the Analysis?
A single storm can generate claims across a whole region, unlike independent losses spread among unrelated policyholders. Shared exposure makes catastrophe risk different from many small, separate claims.
Catastrophe losses can be spatially correlated, so one event may affect many insured properties at once. They can also have fat-tailed loss distributions, which include the possibility of severe events.
Why correlated losses challenge insurance
Insurance works more easily when losses are random, quantifiable, and determinable. Incentives should not create unmanageable adverse selection or moral hazard, and supply must meet demand at a viable price.
A large event does not, by itself, prove that the underlying risk estimate changed. A market shift after a disaster can also reflect capital, reinsurance supply, demand, or regulation.
Hard-market periods followed Hurricane Andrew in 1992, the Northridge earthquake in 1994, and the September 11, 2001 terrorist attacks. Those shifts show that market conditions can change alongside views of risk.
What can prompt a revised risk estimate
Three conditions can justify revising an estimate: prior data was limited, evidence shows the loss distribution is changing, or the team finds an exposure it had not recognized.
Climate-related changes may affect the assumptions used to estimate future losses. Teams should compare newer evidence with the prior view instead of treating one event as a complete trend.
Risk mitigation strategies may reduce damage even when the hazard remains. The analysis should separate what changed in the threat from what changed in prevention, insurance supply, or demand.
When a severe event occurs, teams can test whether the model captured its causes and scope. A fresh estimate should reflect evidence about the hazard, not only the size of one claim season.
Separate new evidence about the hazard from temporary changes in capital, reinsurance supply, or demand before changing an estimate.
How Should Insurers Assess Cybersecurity and Emerging Technology?
A model can improve an underwriting decision only if the data feeding it and the systems protecting it are governed. Good governance links technical controls with clear responsibility.
The NIST Cybersecurity Framework (CSF) 2.0, published February 26, 2024, has six functions: Govern, Identify, Protect, Detect, Respond, and Recover. The framework describes outcomes, not one required way to reach them.
Use a structured cybersecurity framework
Organizations can compare current and target outcomes with Organizational Profiles. Tiers describe the rigor of governance and management practices.
The CSF is designed for organizations of any size, sector, or maturity. Cybersecurity risk assessment methodologies can pair its outcome-based structure with a separate process for identifying and evaluating risks.
NIST CSF 2.0’s six functions do not assign a universal risk score. A team still needs clear criteria to judge the likelihood and impact of threats to its systems and operations.
Govern third-party data and emerging technology
Insurers should review access, data quality, model governance, human review, and accountability when they use outside data. A weak vendor control can affect pricing or underwriting even if the insurer’s own systems remain secure.
Human reviewers need enough detail to question a result and explain a decision. Teams should document who approved material model changes and how they checked the data.
In 2026, the NAIC planned to pilot an AI evaluation tool and expand regulator education and training on emerging technologies. At its 2026 Summer National Meeting, a working group exposed a proposed framework for third-party vendors used in P&C pricing and underwriting.
Keep a named owner responsible for validating material third-party data and model changes.
How Do ERM, ORSA, and Capital Fit Together?
An enterprise view connects individual exposure assessments to strategy, performance, and financial resilience. That connection helps leaders see how separate risks may affect the whole insurer.
Enterprise risk management (ERM) organizes risks across an organization rather than reducing them to one score. COSO’s framework, updated in 2017, has five components and 20 principles.
Connect enterprise risk to strategy
COSO’s five components are governance and culture, strategy and objective-setting, performance, review and revision, and information, communication, and reporting. Together, they connect risk choices to how the business sets goals and measures results.
Governance and culture shape roles and expected behavior. Strategy and objective-setting link plans to risk, while performance identifies and responds to risks that could affect those goals.
Review and revision help leaders adjust as results or conditions change. Information, communication, and reporting carry risk findings to people who must act on them.
ERM can bring together underwriting, operations, investments, and technology risks. That wider view helps leaders compare trade-offs and plan resources without assuming every risk can be removed.
Test long-term viability through ORSA
Own Risk and Solvency Assessment (ORSA) is an insurer’s forward-looking process for analyzing long-term business viability. It considers the risk management and financial resources needed beyond the period used to set regulatory capital requirements.
The IAIS Insurance Core Principle 16 calls for regular ORSAs and ongoing, integrated risk identification, measurement, reporting, and management. ORSA’s long-term viability review connects assessments with the insurer’s enterprise risk management.
An ORSA can help leaders test whether planned business growth fits their risk profile and available resources. It can also show where capital or risk controls may need attention over a longer horizon.
Risk reporting gives decision-makers a shared view of exposures, limits, and changes. Those reports help connect individual assessment findings to financial planning, not just to a compliance file.
Use ORSA to test whether the insurer’s risk management and available resources remain adequate over its longer-term business horizon.
How Do Assessment Results Shape Coverage and Regulation?
An assessment becomes operational when it changes a coverage term, a control, a price, or a capital decision. Actionable findings can lead an insurer to accept, modify, or reject a risk.
Policyholders may also be asked to improve safeguards. Findings can inform limits, deductibles, premiums, reserves, and capital decisions, depending on the insurance line and the decision at hand.
A gross premium can include five main components:
- Expected losses
- Administrative costs
- Acquisition costs
- Reinsurance costs and risk premiums for volatility or catastrophe losses
- Profit margin
For auto coverage, driving history and coverage gaps can affect eligibility and premiums. When comparing high-risk auto insurance offers, match limits and review exclusions, fees, and policy terms.
Organizations also use the four Ts of risk management: tolerate, treat, transfer, and terminate. Labels and decision criteria may differ, so teams should define what each choice means in their setting.
In 2026, the NAIC adopted new C-1 asset-risk factors for collateralized loan obligations, collateralized bond obligations, and collateralized debt obligations. The factors apply to the Life Risk-Based Capital formula at year-end 2026, not to P&C property underwriting.
Check that any regulatory capital change is being applied to the correct insurance line and formula.
How Do We Keep Risk Assessments Current and Actionable?
A risk assessment becomes stale when its assumptions outlive the operations or exposures they describe. Regular ownership helps keep findings tied to real conditions.
Assign a named owner to each material exposure and record review triggers. Track changes in claims, operations, vendors, technology, climate exposure, and capital conditions.
Early-warning monitoring can flag changes before the next scheduled review. Claims trends, new loss reports, or shifts in operating data may call for a closer look.
Monitoring does not replace human review. A person should assess material findings, check whether the evidence is sound, and decide whether the rating or action needs to change.
The NAIC’s 2026 strategic priorities include stronger capital and investment frameworks, more data and analytics for early-warning monitoring, and attention to catastrophe and climate risks. They also include oversight of cybersecurity and insurers’ use of technology and data.
A clear review trigger can be a new vendor, a major change in operations, or evidence that a control no longer works. Teams should record who will review the trigger and what evidence they need.
Set a named owner and a clear trigger for reassessing each material exposure.
Set a named owner and a clear trigger for reassessing each material exposure.
Conclusion
A useful assessment is not the most complicated one, but the one that leads to a defensible decision. Reliable evidence, clear ownership, and regular review help keep that decision useful as conditions change.
Choose one material exposure and record its likelihood, impact, evidence, current control, and reassessment trigger in the risk register. This gives the team a specific finding to review rather than a vague goal to improve risk management.
Start with one material exposure and document who will review it when its assumptions change.